🔥 FREE PRO OFFER OnlyLink.click Pro Version is 100% Free of Cost till 31 December, 2026! Claim Free Pro

Web Development

How WebSockets Work: A Complete Real-Time Connection Walkthrough

How WebSockets Work: A Complete Real-Time Connection Walkthrough

In the early days of the web, the browser was a simple document viewer. You requested a page, the server rendered it, and the connection closed. This request-response cycle is the core of HTTP (Hypertext Transfer Protocol). However, as web applications evolved into rich, interactive experiences—like real-time chat, live financial tickers, collaborative editing, and multiplayer gaming—the traditional HTTP model began to show its limitations. To get live updates, developers initially relied on workarounds:
WebSockets Web Development Networking Real-Time Security
Demystifying Cryptographic Hashing: Why It’s Irreversible and How It Secures Your Passwords

Demystifying Cryptographic Hashing: Why It’s Irreversible and How It Secures Your Passwords

In the world of cybersecurity, hashing is one of the most fundamental yet misunderstood concepts. It is the invisible shield that protects your passwords, verifies the integrity of your downloads, and powers the blockchain. But what exactly is a hash? Why can’t we “decrypt” it? and most importantly, if it’s irreversible, how does a website know you’ve entered the right password?
Security Cryptography Hashing Passwords Cybersecurity Web Development
Web Security Essentials: SSRF, CSRF, and CORS Explained

Web Security Essentials: SSRF, CSRF, and CORS Explained

In the modern web landscape, security is not just a feature—it’s a foundation. As applications become more interconnected, understanding the nuances of how requests are handled across different origins and servers is crucial for any developer. Today, we’re diving into three critical concepts that every web developer should master: SSRF, CSRF, and CORS. While they might sound like alphabet soup, they represent the front lines of web application security.
Security Web Development SSRF CSRF CORS DevSecOps
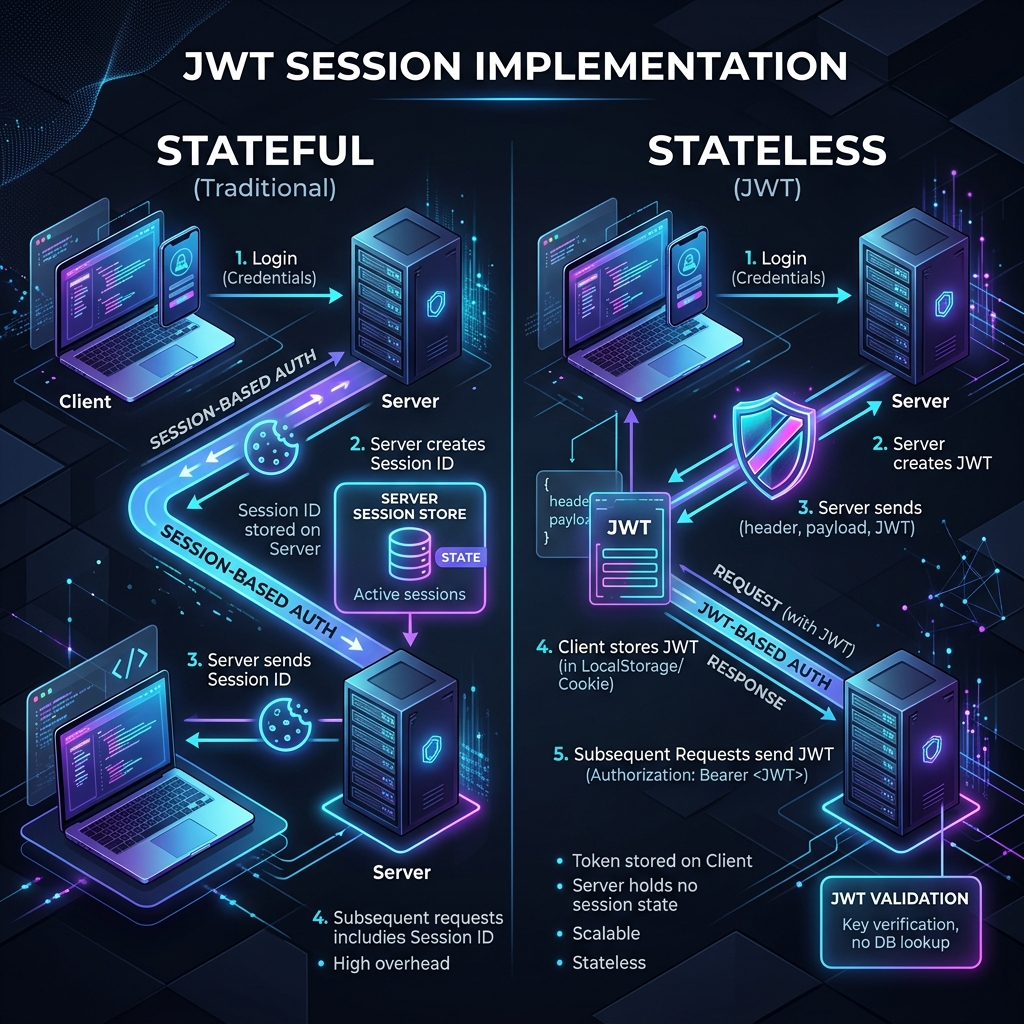
JWT Session Token Implementation: Stateful vs. Stateless

JWT Session Token Implementation: Stateful vs. Stateless

JSON Web Tokens (JWT) have become the industry standard for securely transmitting information between parties as a JSON object. When it comes to session management, developers often face a critical architectural decision: Should the implementation be Stateless (without state) or Stateful (with state)? Both approaches have their merits, and choosing the right one depends entirely on your application’s scale, security requirements, and infrastructure.
JWT authentication security web development session management dev-tools